OSCP vs. Red Team: Choosing the Right Cybersecurity Path
If you’ve ever stared at a list of cybersecurity certifications and wondered which one will set your career on fire, you’re not alone. The OSCP (Offensive Security Certified Professional) and the Red Team track are two of the most talked‑about routes, but they’re not interchangeable. In the next few hundred words we’ll compare their core demands, typical job roles, learning curves, and even earning potential so you can decide which path feels right for you.
What Exactly Is the OSCP?
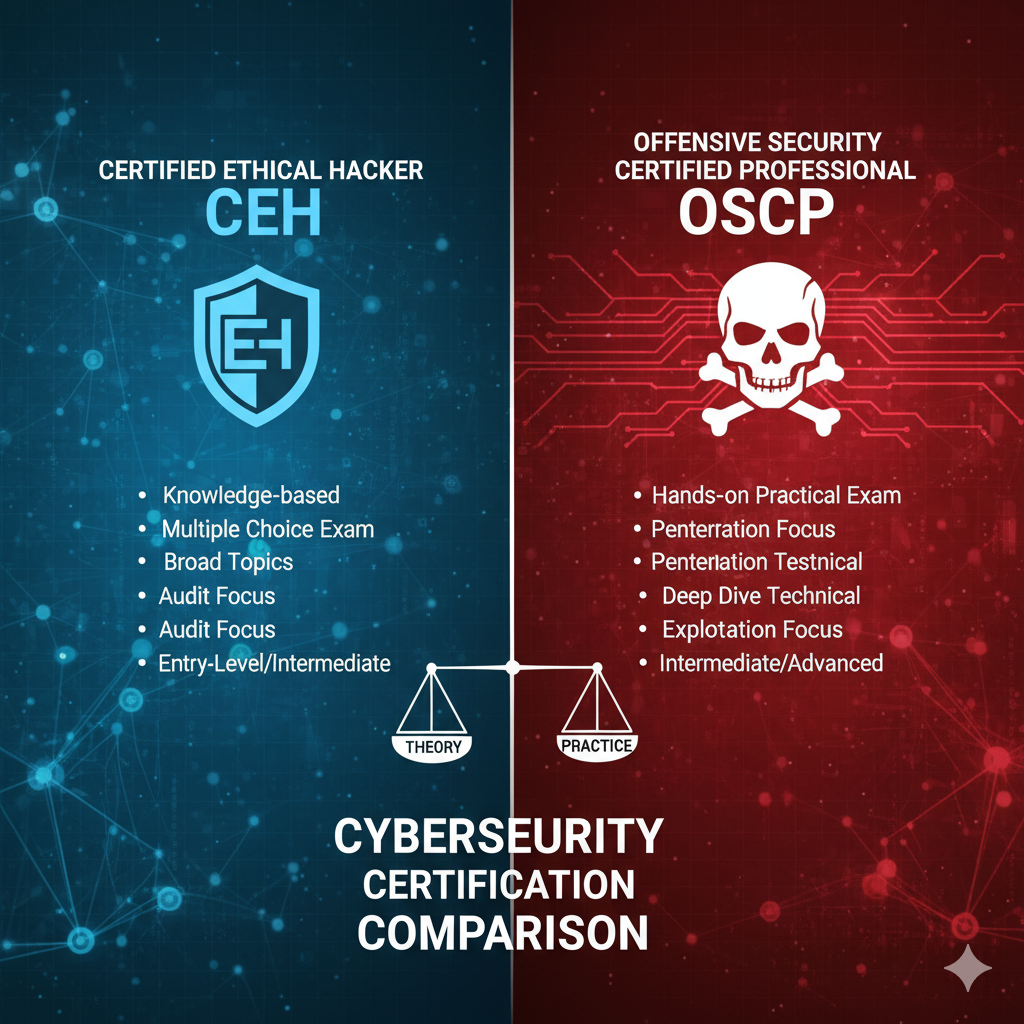
The OSCP is an exam‑based certification that focuses on hands‑on, real‑world penetration testing. Candidates learn to identify vulnerabilities, exploit them, and document their findings in a detailed report. The exam itself is a 24‑hour practical test where you’re given a virtual lab environment and must compromise multiple machines. Successful completion earns you a certificate that is highly respected in the industry for demonstrating tangible hacking skills.
The Red Team Landscape
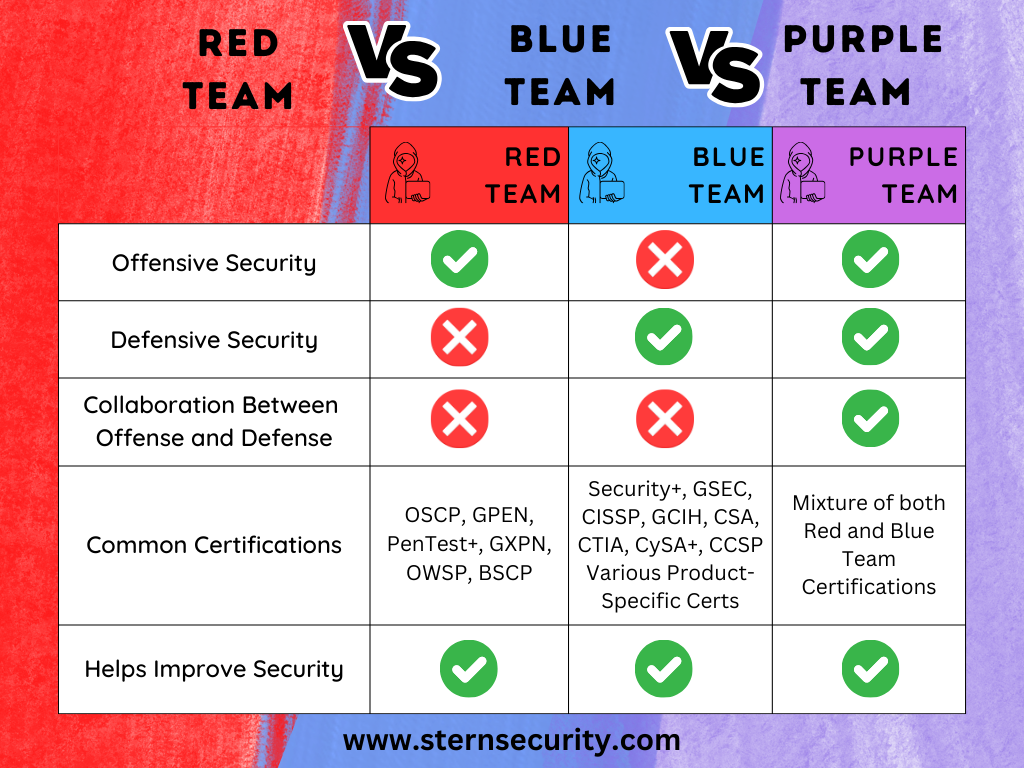
Red Team work is broader. It’s not just about breaching a single system; it’s about emulating advanced adversaries to test an organization’s security posture from end to end. Red Teamers use the same tools as penetration testers but combine them with social engineering, physical security bypasses, and threat‑simulation frameworks. The goal is to surface systemic weaknesses rather than isolated vulnerabilities.
Comparing Core Competencies
Technical Focus
- OSCP: Network exploitation, privilege escalation, exploitation of known weaknesses.
- Red Team: Adversary emulation, lateral movement, persistence, and stealth.
Toolset and Methodology
- OSCP: Metasploit, Nmap, Burp Suite, custom scripts.
- Red Team: All OSCP tools plus advanced frameworks like ATT&CK, Mimikatz, custom backdoors, and often physical tools.
Reporting Style
- OSCP: Technical report focused on exploit steps and remediation.
- Red Team: Narrative‑driven, highlighting business impact and recommending defensive hardening.
Career Trajectories and Earnings
Penetration testers—often OSCP holders—typically work for consulting firms, government agencies, or in-house security teams. Red Teamers, on the other hand, may be embedded in larger enterprises, security divisions, or specialized red‑team consultancies. While salaries vary widely, the trend shows that Red Team roles can command higher pay for the added strategic depth. For instance, a junior penetration tester might earn $70k–$90k, whereas a junior red teamer could start between $85k and $110k, depending on the organization and location.
Education and Time Investment
The OSCP is a relatively short, intense program. Most candidates dedicate 4–6 months to the course, labs, and practice exams. The focus is narrow and repeatable. In contrast, building a solid Red Team skillset takes longer. Many professionals combine the OSCP with additional certifications—such as the GIAC Red Team Essentials (GCTE) or Certified Red Team Professional (CRTP)—and spend months learning social engineering, physical security, and advanced adversary emulation.
Which Path Aligns With Your Goals?
Consider the following:
- Hands‑on hacking vs. strategic defense: Are you fascinated by the mechanics of exploitation, or are you more drawn to thinking like a sophisticated attacker to protect an organization?
- Solo work vs. team play: OSCP training often involves individual practice, whereas Red Team operations require close collaboration with other red and blue team members.
- Immediate impact vs. long‑term planning: Pen testing typically yields quick fixes. Red Teaming uncovers systemic risks that may need multi‑year remediation.
Hybrid Paths: Combining OSCP and Red Team Skills
Many professionals start with an OSCP to establish a strong technical foundation and then expand into Red Team roles. The OSCP’s rigorous labs build discipline; the red‑team experience adds strategic thinking. Some organizations even award a higher tier of certification for professionals who have both an OSCP and a proven red‑team track record.
FAQ
- Can I use OSCP skills in a Red Team role? Yes, the technical prowess gained during OSCP training is directly applicable to the exploitation phase of Red Team exercises.
- Do I need a formal Red Team certification after getting the OSCP? Not necessarily, but additional credentials—like GCTE or CRTP—can boost credibility and show commitment to the broader red‑team discipline.
- Which path is easier to break into? Penetration testing tends to have a lower barrier to entry because of the focused skill set. Red Team roles often require broader knowledge and more experience.
- Is the OSCP worth the investment? Many security professionals find the OSCP’s reputation and hands‑on approach to be a worthwhile investment, especially if you aim for a penetration testing career.