Optimizing OSPF Interface Costs on FortiGate: Tips & Best Practices
When a FortiGate firewall participates in an OSPF area, the cost you assign to each interface can make or break traffic engineering plans. A mis‑set cost might push routes through a suboptimal path, or—worse—cause routing loops that jeopardize security policies. This guide walks through the essential steps for FortiGate OSPF interface cost configuration and shares practical best practices to keep your network both efficient and reliable.
Understanding OSPF Interface Cost on FortiGate
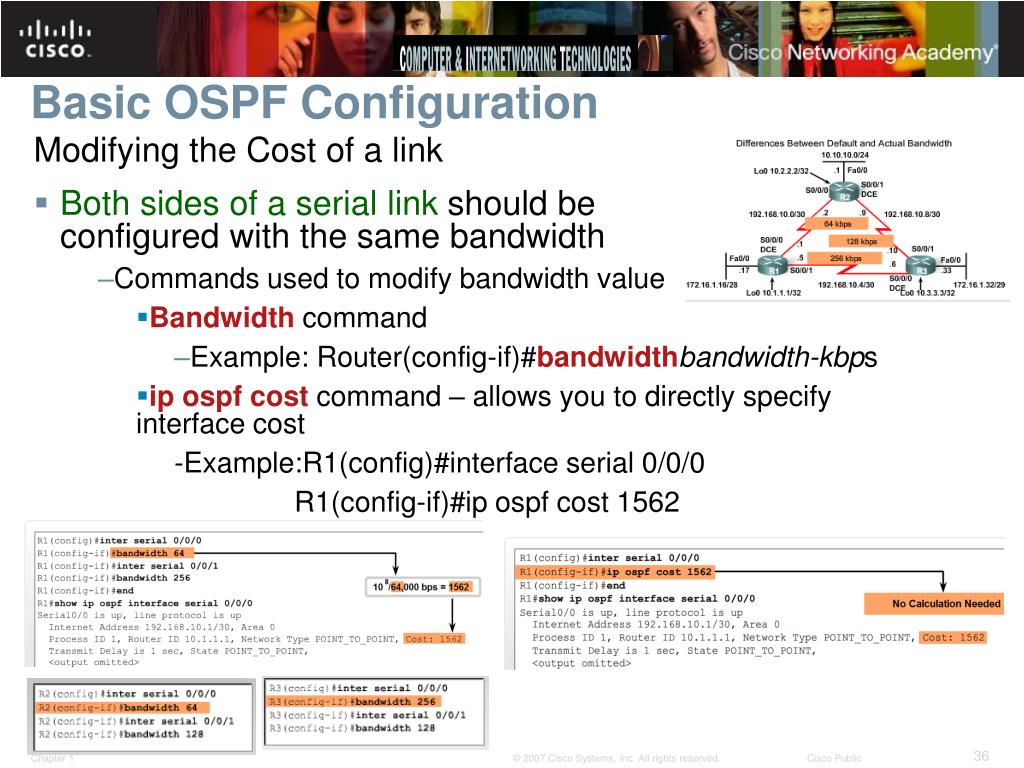
OSPF calculates the best route based on the sum of costs along a path. By default, FortiGate derives the cost from the interface’s bandwidth, using a formula of 10^8 divided by the bandwidth in bits per second. While this works for many environments, it often falls short when you need finer control over traffic flow.
Key points to remember:
- Cost is a relative metric. A lower cost attracts traffic; a higher cost pushes it away.
- All routers in the same area must agree on cost values. Inconsistent settings can fragment the SPF calculation.
- FortiGate allows manual overrides. You can set a static cost per interface, overriding the automatic calculation.
Step‑by‑Step Configuration
Below is a concise walk‑through for adjusting interface costs via the GUI and the CLI. Choose the method that fits your workflow.
Using the FortiGate GUI
- Log into the FortiGate web UI and navigate to Network > Interfaces.
- Select the interface you want to modify, then click Edit.
- Under the OSPF tab, locate the Cost field. Enter a numeric value that reflects the desired metric—common practice is to use multiples of 10 for easy readability.
- Save the changes and repeat for any additional interfaces.
Using the CLI
- Enter configuration mode:
config router ospf - Select the area that contains the interface:
edit 0 (replace0with your actual area ID) - Specify the interface and set the cost:
config interface
edit port1
set cost 20
next
end - Commit the changes with end and verify with show router ospf.
After any change, run get router info ospf neighbor to confirm that OSPF neighbors have converged with the new cost values.
Common Pitfalls and How to Avoid Them
Even seasoned engineers stumble over a few recurring issues when tweaking OSPF costs on FortiGate devices.
- Overlooking default bandwidth settings. Some interfaces (like tunnel or VLAN interfaces) report a default bandwidth of 1 Gbps, which translates to a cost of 100. If you forget to adjust this, the cost may be lower than intended.
- Mixing static and dynamic costs. If you manually set a cost on one interface but leave another at its calculated value, the network may favor the static route unexpectedly.
- Neglecting OSPF redistribution. When you redistribute routes from other protocols, FortiGate applies the interface cost to the redistributed metric. Double‑check the redistribution settings to avoid inflated metrics.
To sidestep these traps, document each interface’s intended role, verify bandwidth assumptions, and run a quick diagnose ip route list ospf after changes.
Best‑Practice Recommendations
Implementing a consistent cost strategy pays dividends in both performance and troubleshooting. Here are proven practices that align with FortiGate’s design philosophy.
- Adopt a tiered cost model. Assign a base cost (e.g., 10) to core uplinks, a higher cost (e.g., 20‑30) to secondary links, and a much higher cost (e.g., 100+) to backup or low‑bandwidth paths. This hierarchy makes intent clear at a glance.
- Document cost values alongside link specifications. Keeping a spreadsheet that maps each interface to its bandwidth, physical media, and OSPF cost reduces accidental mismatches during upgrades.
- Leverage interface groups for uniformity. If several interfaces share the same role, use a FortiGate interface group and apply the same cost configuration in one step.
- Test changes in a lab or staged environment. Before rolling out cost adjustments network‑wide, simulate the change on a single FortiGate or a virtual instance to observe SPF recalculation times and verify that traffic follows the expected path.
- Monitor OSPF convergence after each tweak. Use
get router info ospf databaseandget router info ospf neighborto ensure all routers have a consistent view of the topology. - Combine cost tuning with route‑maps where needed. For granular control—such as preferring a specific path for certain subnets—pair static costs with OSPF route‑maps to influence metric calculations without altering interface settings globally.
FAQ
What happens if I set the OSPF cost to zero on a FortiGate interface?
OSPF treats a cost of zero as the lowest possible metric, effectively making that interface the preferred route for all traffic in the area. While this can be useful for a designated primary link, it may overload the interface and cause unintended congestion.
Can I use different OSPF costs for IPv4 and IPv6 on the same FortiGate interface?
Yes. FortiGate maintains separate OSPFv2 (IPv4) and OSPFv3 (IPv6) processes, each with its own cost configuration. Be sure to set the cost in the appropriate OSPF section to avoid mismatches.
Is there a recommended maximum OSPF cost value on FortiGate?
OSPF cost values are 32‑bit integers, so technically you can use very large numbers. Practically, most engineers keep costs below 65535 to stay within the range commonly supported by legacy routers and to keep configuration readable.
How often does FortiGate recalculate OSPF costs after a change?
Once you commit a new cost, FortiGate triggers an immediate SPF run. Neighbors receive updated LSAs within a few seconds, and the network converges based on the new metrics.