Master IP Address Matching with Scprefix and Listsc: A Practical Guide
Why IP Address Matching Matters in Modern Networks
Every day, network administrators and security analysts rely on accurate IP address matching to isolate traffic, enforce policies, and detect anomalies. A single misconfigured rule can expose services to attack, while an overly broad rule can block legitimate users. Mastering the tools that make matching fast and reliable—especially Scprefix and Listsc—translates directly into more secure, efficient operations.
Getting Started: The Role of Scprefix in Address Matching
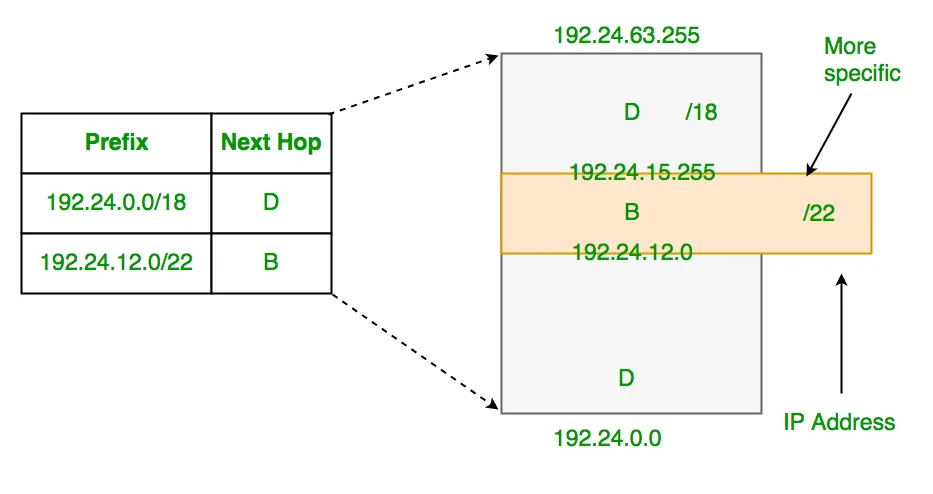
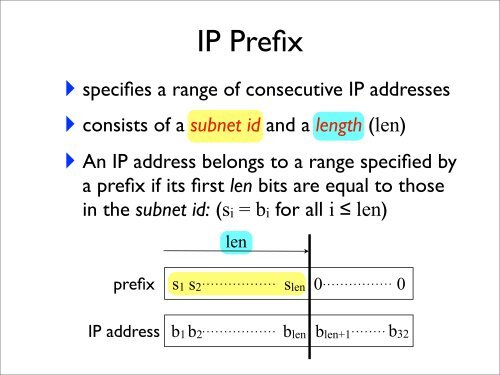
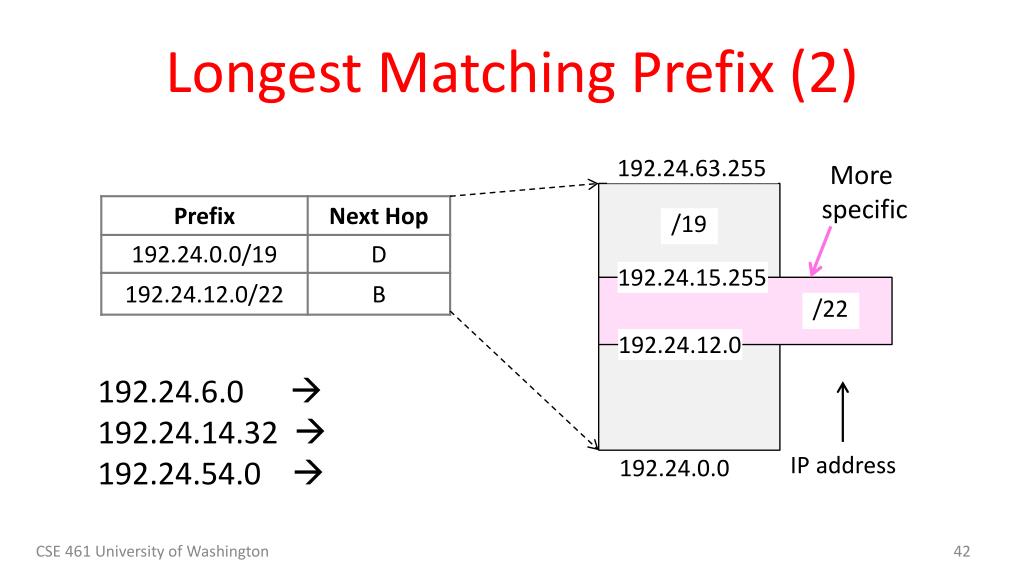
Scprefix is a lightweight prefix-matching engine built into many security frameworks. It stores CIDR blocks in a trie structure, allowing lookup times that are independent of the number of prefixes. In practice, this means you can maintain thousands of subnets without sacrificing performance.
Typical usage follows a simple pattern:
- Load the prefix list into Scprefix via a configuration file or API call.
- Query the engine with an IP address to receive a boolean result or the matching prefix.
- Chain the result into a policy decision or logging mechanism.
Because Scprefix is deterministic, you can reproduce results across distributed systems, a critical property for compliance audits.
Integrating Listsc: Organizing and Querying Complex Rules
Listsc complements Scprefix by providing a higher-level abstraction for rule sets. While Scprefix deals with the raw address matching, Listsc handles metadata, tagging, and conditional logic. A Listsc rule might look like:
- allow 192.168.1.0/24 if role = "web"
- deny 10.0.0.0/8 if threat_level > 5
When Listsc processes a packet, it first delegates the IP lookup to Scprefix. The matching prefix is then combined with the rule's tags to decide whether to allow or block the flow.
Loading Rules Efficiently
Both Scprefix and Listsc can consume large rule files. To avoid startup bottlenecks:
- Pre‑compile prefix files into binary formats if the platform supports it.
- Split rule sets into logical groups—e.g., internal, external, DMZ—and load only the relevant group at runtime.
- Use incremental updates: instead of reloading the entire file, push deltas that add or remove specific prefixes.
Practical Use Cases
1. Firewall Policy Enforcement: Combine Scprefix for IP checks with Listsc to attach service tags. The firewall can quickly drop packets from known malicious subnets while allowing traffic for whitelisted services.
2. Intrusion Detection Systems (IDS): An IDS can query Scprefix to confirm that an incoming connection originates from a protected subnet. Listsc then checks whether the connection aligns with threat signatures before raising alerts.
3. Compliance Auditing: Generate reports that list all IP addresses that matched a particular policy over a period. Scprefix ensures the data set is accurate, and Listsc provides the context needed for audit logs.
Advanced Matching Techniques
While Scprefix excels at prefix matching, complex scenarios require more flexibility.
Negative Prefixes (Exclusions)
Some security policies need to exclude specific IP ranges from a broader block. Scprefix allows negative prefixes by storing a separate exclusion trie. During lookup, the algorithm checks the inclusion trie first, then verifies that the address does not appear in the exclusion trie.
Multiple IP Versions
Modern networks often carry both IPv4 and IPv6 traffic. Scprefix supports both families natively. Listsc rules can reference either version by using a generic ip_version tag, ensuring consistent handling across protocols.
Performance Tuning
To maintain low latency in high‑traffic environments:
- Keep the prefix list under 1 GB when possible; larger lists may require sharding.
- Use memory-mapped files for read‑only prefix data.
- Profile the lookup path regularly; the first few microseconds can dominate overall processing time.
Troubleshooting Common Pitfalls
- False Negatives: Verify that the CIDR notation is correct. A missing slash or an extra digit can silently exclude a subnet.
- Cache Invalidation: If Listsc uses caching, stale entries can lead to outdated policy decisions. Ensure that the cache expires after rule updates.
- Load Imbalance: In distributed deployments, uneven distribution of prefixes across nodes can cause bottlenecks. Use consistent hashing to balance the load.
Best Practices for Long‑Term Maintenance
- Version Control: Keep rule files in a Git repository. Tag releases that correspond to network policy changes.
- Automated Testing: Write unit tests that feed known IP addresses and assert the expected policy outcome. Run these tests on every commit.
- Documentation: Maintain a living document that explains each rule group, its purpose, and its risk profile.
- Monitoring: Log lookup counts and hit rates. Sudden drops in hit rates may indicate a misconfigured prefix list.
FAQ
Q1: What is the difference between Scprefix and Listsc?
A1: Scprefix is a low‑level prefix lookup engine that quickly determines whether an IP address falls within any stored CIDR block. Listsc is a higher‑level rule engine that associates prefixes with metadata and conditional logic to enforce policies.
Q2: Can Scprefix handle IPv6 addresses?
A2: Yes, Scprefix supports both IPv4 and IPv6. The trie structure is agnostic to address length, allowing efficient lookup for either family.
Q3: How do I add a new subnet to an existing Scprefix database?
A3: Append the new CIDR to the source file, then recompile or reload the trie. If the platform supports incremental updates, push the new prefix as a delta.
Q4: Is it safe to use Listsc in a high‑availability firewall?
A4: When configured with