How to Safely Sync iOS Core Data Using PowerShell & MTLS
When a mobile app needs to push local iOS Core Data records to a backend, the temptation is to use a quick HTTPS call. In production environments, however, that approach often leaves sensitive payloads exposed or difficult to audit. By pairing Core Data with PowerShell automation and a mutual TLS (MTLS) handshake, you get an end‑to‑end pipeline that is both auditable and resistant to man‑in‑the‑middle attacks. This article walks through the concepts, the setup, and the scripts you’ll need to make the trio work together.
Why Combine iOS Core Data with PowerShell and MTLS?
Core Data is great at modeling complex object graphs on the device, but it doesn’t dictate how those objects travel off‑board. PowerShell, traditionally a Windows admin tool, shines when you need to orchestrate file transfers, certificate handling, or REST calls from a server. MTLS adds a cryptographic layer where both client and server prove their identities, turning a simple TLS tunnel into a two‑way trust relationship. When you blend these three, you gain:
- Fine‑grained control over when and how data leaves the phone.
- Automated certificate rotation without manual keystrokes.
- Clear audit trails that can be logged on the PowerShell side.
Understanding the Pieces: Core Data, PowerShell, and MTLS
Core Data in a Nutshell
At its core, Core Data is an object graph manager that can persist to SQLite, binary, or in‑memory stores. It abstracts fetch requests, relationships, and change tracking so developers can think in terms of entities rather than SQL. When you need to export data, you typically fetch the managed objects, serialize them (often to JSON), and hand the payload off to a network layer.
PowerShell’s Role in Automation
PowerShell isn’t limited to Windows; with PowerShell 7+ it runs cross‑platform, meaning you can host scripts on a Linux or macOS backend as well. Its cmdlets for Invoke‑RestMethod, Import‑PfxCertificate, and secure string handling make it a natural fit for building a wrapper that receives the JSON, validates it, and forwards it to an MTLS‑protected endpoint.
What Makes MTLS “Secure”?
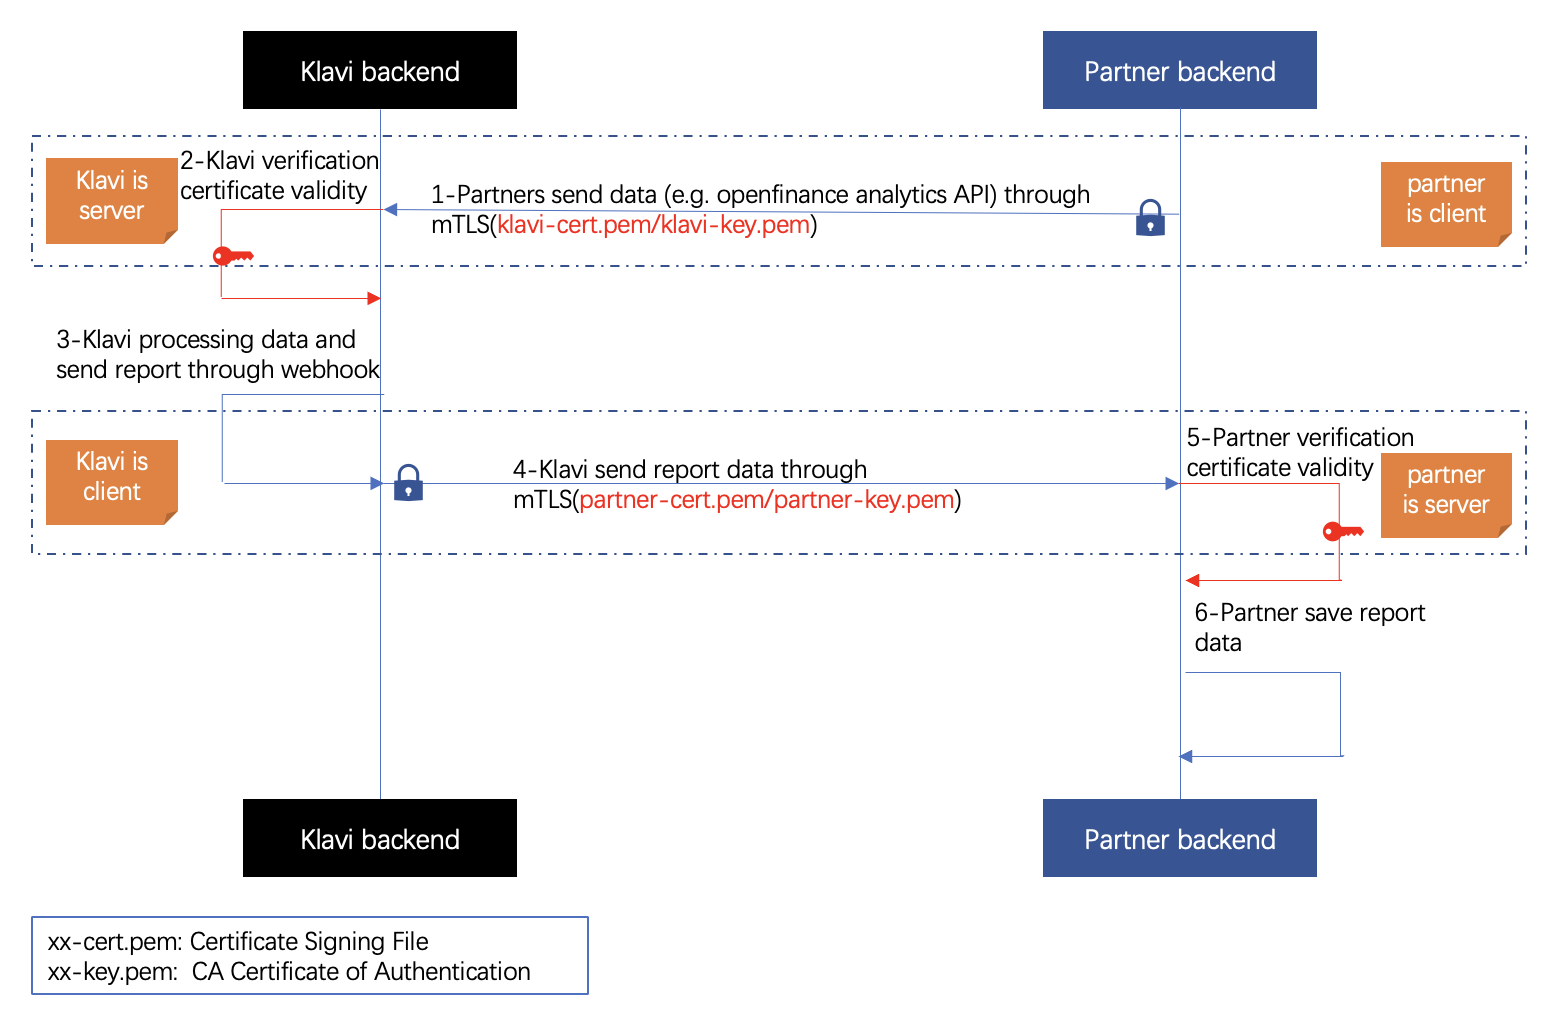
Standard TLS authenticates the server to the client. MTLS adds a client certificate, so the server also verifies the caller. This mutual verification eliminates the risk of an impostor client sending bogus data, because the server will reject any request lacking a valid, signed certificate from a trusted authority.
Setting Up a Secure MTLS Pipeline
Before you write any code, you need a certificate hierarchy that both iOS and the PowerShell host trust.
- Step 1 – Create a Root CA. Use OpenSSL or your corporate PKI to generate a self‑signed root certificate.
- Step 2 – Issue Server and Client Certificates. Sign a server certificate for
api.example.comand a client certificate for the iOS app. Export the client cert as a PKCS#12 bundle (pfx) with a strong password. - Step 3 – Distribute the Client Cert. Embed the pfx in the app bundle (encrypted) or fetch it securely from the device’s keychain at first launch.
- Step 4 – Install the Root CA on the Server. Add the root cert to the trusted store of the web server handling the MTLS endpoint.
Once the certificates are in place, the server will only accept connections that present the correct client certificate.
PowerShell Scripts to Transfer Core Data Safely
The iOS app can POST its JSON payload to a thin Azure Function or an on‑premise endpoint that simply writes the data to a temporary file. A scheduled PowerShell script then picks up that file, validates the JSON schema, and forwards it to the MTLS API.
- 1. Import the client certificate. Import‑PfxCertificate -FilePath “C:\certs\iosclient.pfx” -Password (ConvertTo‑SecureString “$pwd” -AsPlainText -Force) -CertStoreLocation Cert:\CurrentUser\My
- 2. Build the HTTPS request. Use Invoke‑RestMethod -Method Post -Uri https://api.example.com/ingest -Body $json -CertificateThumbprint $thumbprint -SkipCertificateCheck:$false
- 3. Log the transaction. Append a line to a CSV log with timestamp, payload size, and HTTP status code.
Because PowerShell respects the -CertificateThumbprint parameter, the client cert is automatically attached to the TLS handshake, satisfying the MTLS requirement.
Testing and Verifying the Connection
Start with a local loopback test. Run the PowerShell script against a self‑signed server on localhost that demands MTLS. Use Test‑Connection to confirm the handshake succeeds, and inspect the server logs for the client certificate details. Once the local test passes, move to a staging environment and repeat with the real root CA.
Common Pitfalls and How to Avoid Them
- Certificate Expiration. Automate renewal with a cron job or Azure Key Vault; never rely on a manual update schedule.
- Mismatched Hostnames. The server certificate’s Common Name must match the URL used in Invoke‑RestMethod, otherwise TLS will abort before MTLS even begins.
- Improper JSON Encoding. iOS’s
JSONEncodermay emit dates in ISO8601; ensure the PowerShell side expects the same format, or normalize it before forwarding.
Best Practices for Ongoing Maintenance
Treat the MTLS pipeline as a living component. Regularly audit the certificate store on both iOS and the server for orphaned or revoked certificates. Use PowerShell’s Get‑ChildItem Cert:\CurrentUser\My to list active certs and cross‑check against a central inventory. Additionally, version your Core Data schema and embed a schemaVersion field in the JSON payload; this way, the PowerShell script can reject outdated records before they reach downstream services.
FAQ
Q: Can I use a wildcard certificate for the iOS client?
A: Technically possible, but not recommended. Wildcards broaden the trust surface, making it easier for a compromised app to impersonate another client.
Q: Do I need a separate PowerShell script for each Core Data entity?
A: Not necessarily. A single script can handle a generic JSON envelope that includes an entity type field, routing the payload to the appropriate API endpoint.
Q: What if the device is offline when the data is ready?
A: Queue the JSON locally (e.g., in a “PendingSync” Core Data entity) and trigger the PowerShell upload once network reachability is restored.
Q: Is MTLS supported on iOS without third‑party libraries?
A: Yes. NSURLSession’s URLSession:didReceiveChallenge:completionHandler: delegate lets you supply the client identity from the keychain, enabling native MTLS.