Governance, Risk & Compliance Explained: A Practical Guide
What Is Governance, Risk & Compliance (GRC)?
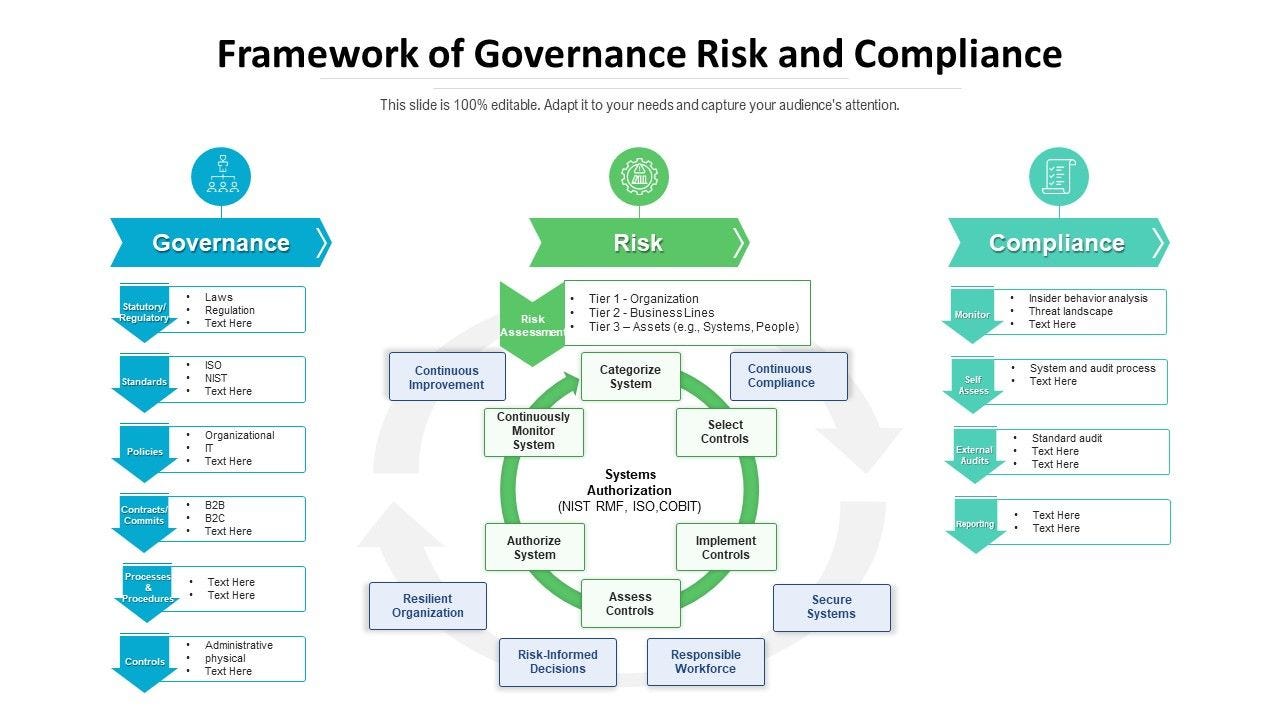
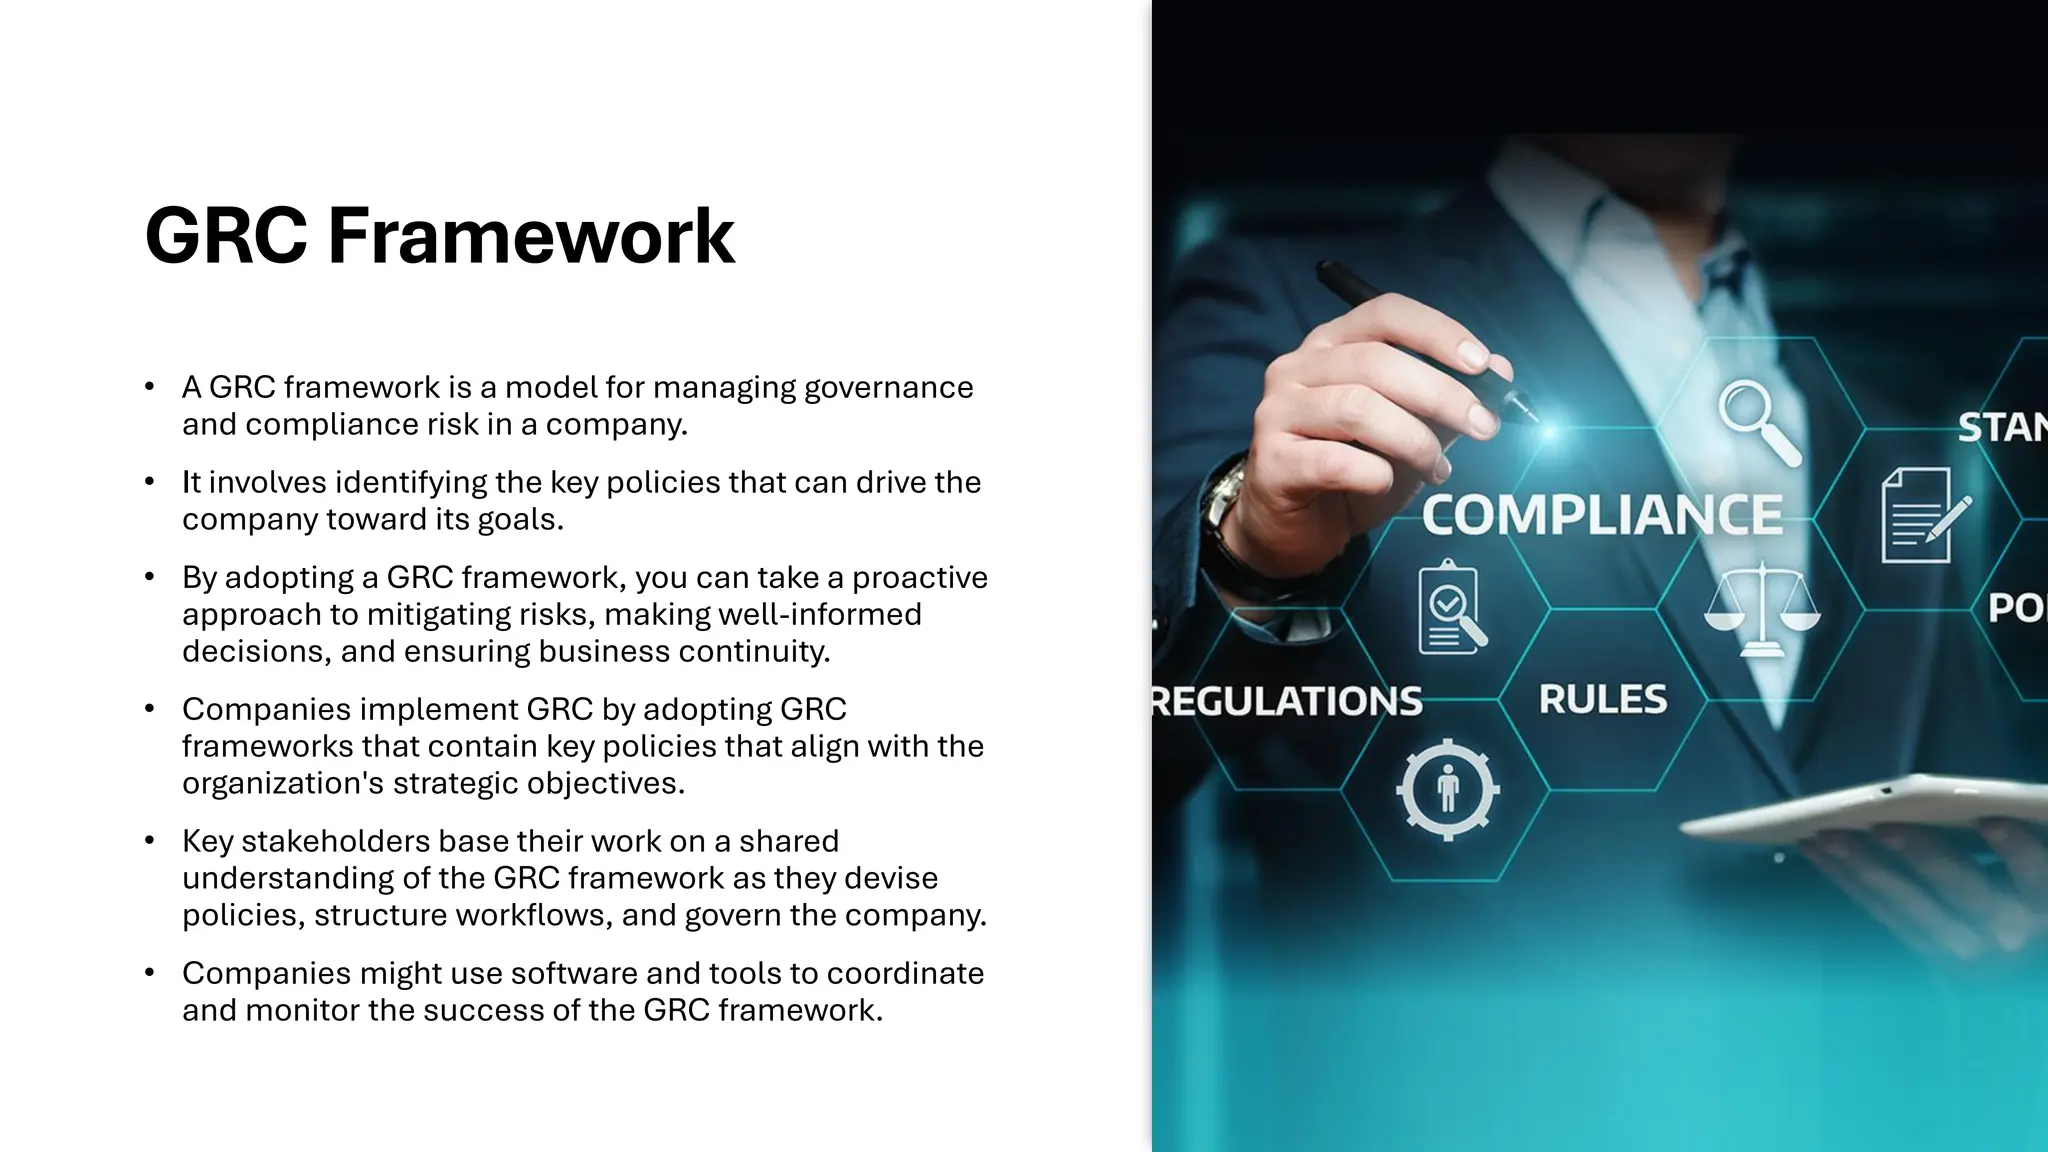
Governance, Risk & Compliance—often abbreviated as GRC—is a framework that helps organizations align their objectives, manage uncertainty, and meet legal or industry standards. In simple terms, governance sets the direction and policies, risk management identifies and mitigates potential threats, and compliance ensures that the rules are actually followed. Together, these three pillars create a structured approach to decision‑making that balances ambition with accountability.
Why Organizations Need a Unified GRC Strategy
Running governance, risk and compliance as separate silos can lead to duplicated effort, conflicting priorities, and costly oversights. A unified GRC strategy consolidates data, streamlines reporting, and provides a single source of truth for senior leadership. This not only reduces operational friction but also improves the organization’s ability to respond to regulatory changes or emerging cyber threats.
Core Components of a Robust GRC Program
- Governance: Defines the policies, roles, and decision‑making structures that guide the business. Think board charters, code of ethics, and performance metrics.
- Risk Management: Involves identifying, assessing, and prioritizing risks—whether strategic, operational, financial, or reputational. Tools like risk registers and heat maps are common.
- Compliance: Tracks adherence to laws, regulations, and internal standards. This includes everything from data‑privacy mandates to industry‑specific certifications.
Getting Started: A Step‑by‑Step Roadmap
1. Assess the current landscape. Map existing policies, risk registers, and compliance checklists. Identify gaps and overlapping responsibilities.
2. Define clear objectives. What does success look like for your GRC effort? Typical goals include reducing audit findings, improving risk visibility, or accelerating regulatory reporting.
3. Choose a technology platform. Modern GRC tools integrate with ERP, HR, and security systems, providing real‑time dashboards. Look for solutions that support role‑based access and automated workflow.
4. Establish governance structures. Create a steering committee, assign owners for each domain, and set up regular review cycles.
5. Roll out training and communication. Employees at all levels need to understand their responsibilities—whether it’s filing a risk incident or following a new policy.
Common Challenges and How to Overcome Them
Many firms stumble when the GRC initiative is seen as a compliance checkbox rather than a strategic asset. To avoid that trap, embed risk considerations into everyday business processes instead of treating them as an after‑thought. Another frequent hurdle is data silos; integrating disparate systems can be technically demanding, but leveraging APIs or a cloud‑based GRC suite often simplifies the task.
Measuring the Impact of GRC
Key performance indicators (KPIs) give life to a GRC program. Typical metrics include the number of open risk items, average time to remediate a compliance issue, and audit cycle duration. Tracking these figures over time reveals trends, highlights improvement areas, and demonstrates ROI to executives.
Resources You Can Download as PDFs
While this article provides a concise overview, many organizations prefer a printable reference. Look for PDF guides that cover GRC best practices, regulatory checklists, or industry‑specific frameworks. Reputable sources—such as the Institute of Internal Auditors, ISO, or major consulting firms—often publish free PDFs that you can adapt to your own processes.
Quick FAQ
Q: Is GRC only for large enterprises?
A: Not at all. Small and mid‑size firms benefit from a scaled‑down GRC approach, focusing on high‑impact risks and the most relevant regulations.
Q: How does GRC differ from simple compliance?
A: Compliance is a component of GRC. Governance adds strategic direction, while risk management provides a proactive lens to anticipate and mitigate threats before they become violations.
Q: Can a single software solution handle all three pillars?
A: Many modern platforms aim to do so, offering modules for policy management, risk assessment, and audit tracking within a unified interface.
Q: How often should a GRC program be reviewed?
A: At a minimum, conduct an annual comprehensive review, with quarterly updates for high‑risk areas or after major regulatory changes.