Fix OCSP Response Not Valid Errors: A Step‑by‑Step Guide
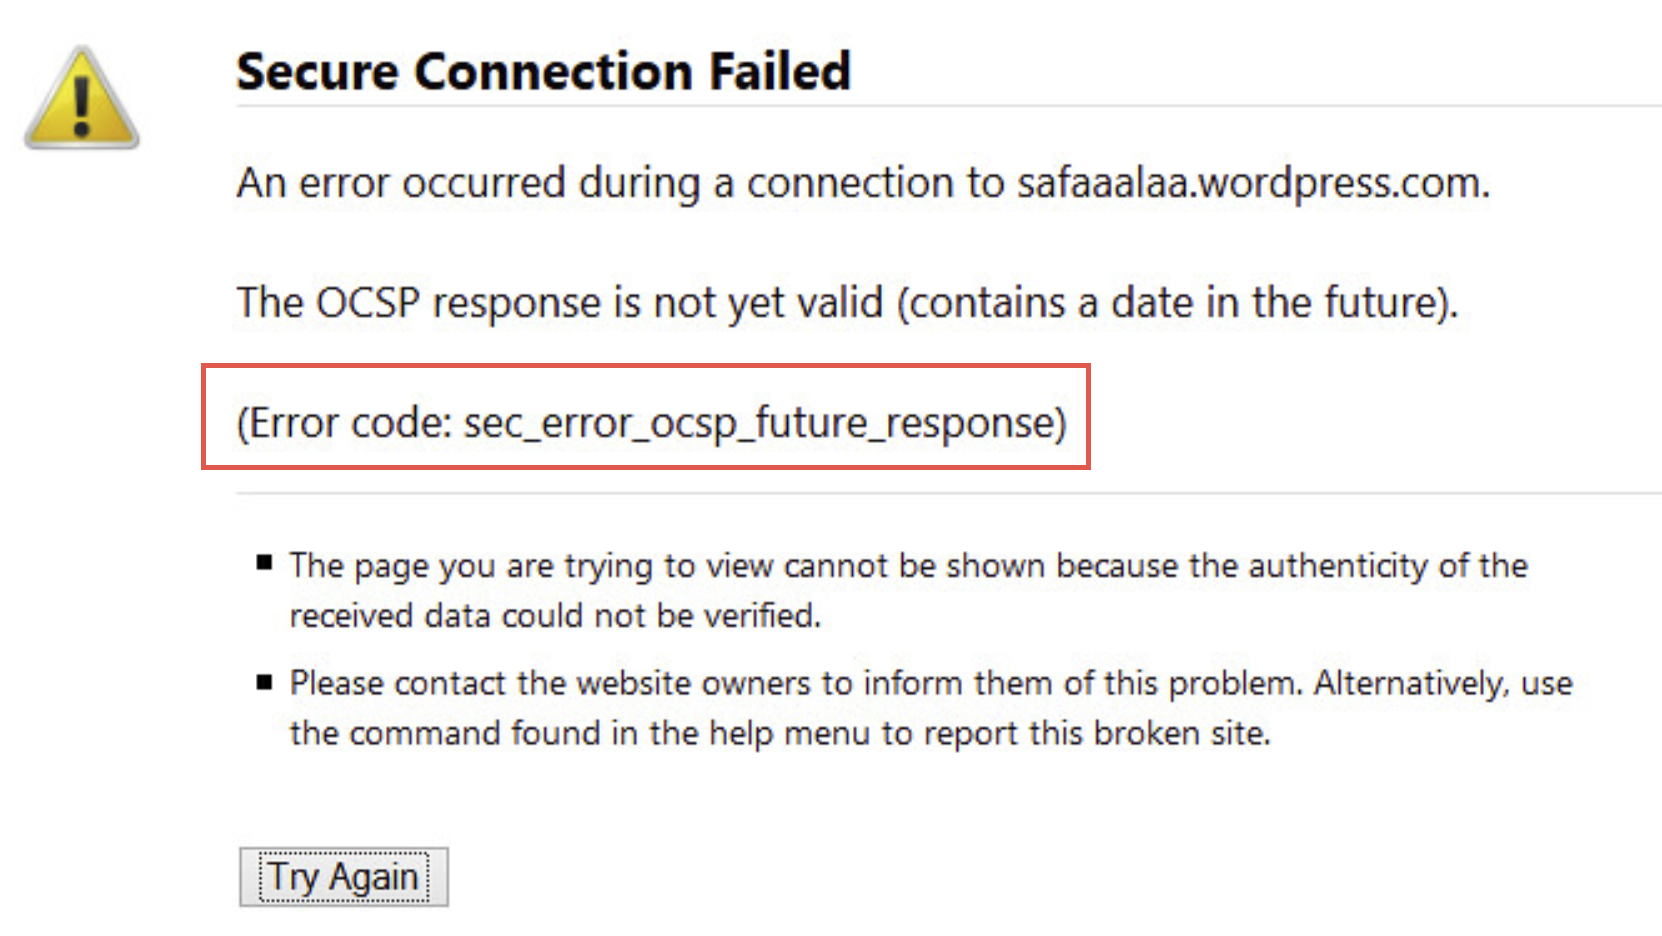
When a browser or application throws an “OCSP response not valid” message, it’s a sign that the Online Certificate Status Protocol (OCSP) check failed to confirm a certificate’s current state. This error can block secure connections, disrupt web services, or prevent software from launching. The good news is that OCSP issues are usually resolvable with a systematic approach. Below is a detailed troubleshooting guide that walks you through diagnosing the root cause, applying corrective measures, and implementing preventive best practices.
Understanding OCSP and the “Not Valid” Error
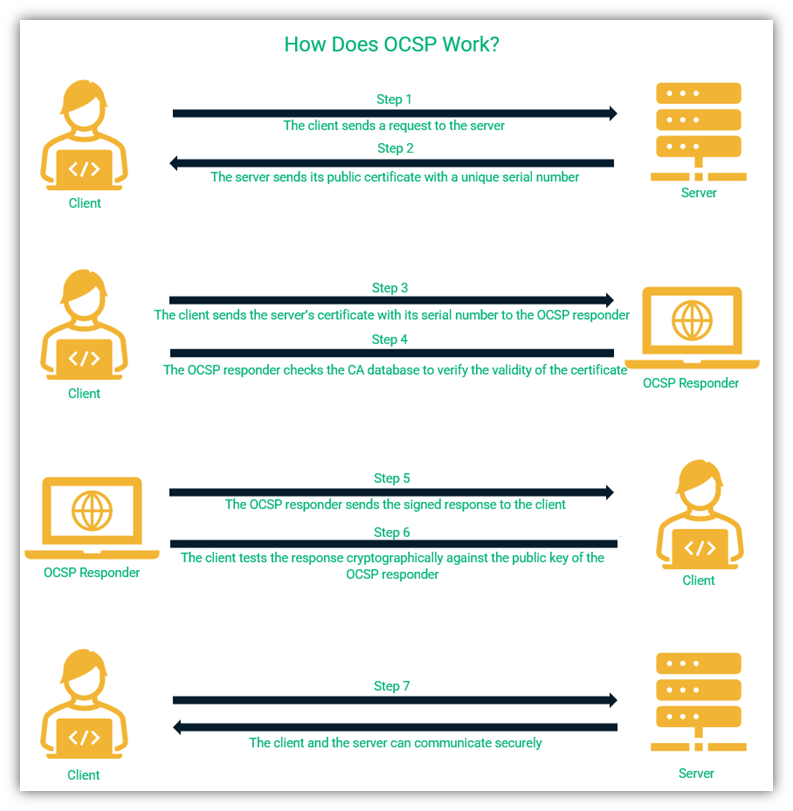
OCSP is a lightweight protocol that lets clients query a certificate authority (CA) to see whether a particular X.509 certificate is revoked. A successful OCSP response confirms the certificate is good, while a failure—such as a “response not valid”—means the client could not obtain or verify a proper status.
Typical scenarios include:
- Expired or malformed OCSP responder URL in the certificate.
- Network blockage preventing reach to the responder.
- Clock drift on the client or responder, causing timestamp validation to fail.
- Misconfigured proxy or firewall filtering OCSP traffic.
Common Causes of OCSP Response Not Valid
1. Incorrect OCSP Responder URL
Certificates embed an OCSP responder URL in the Authority Information Access (AIA) extension. If the URL is misspelled, points to an outdated responder, or uses the wrong protocol, clients will reject the response.
2. Network Connectivity Issues
Firewalls, DNS problems, or routing glitches can block HTTP or HTTPS traffic to the responder. Even a brief outage can trigger the “not valid” message.
3. Time Skew
OCSP responses carry a ProducedAt timestamp. Clients compare this to their local clock. If the client’s clock is off by more than 5 minutes, the response is considered invalid.
4. Unsupported Response Formats
Some responders deliver responses in MIME type application/ocsp-response; others might return application/pkix-cert or even plain text. Clients expecting a strict format may reject them.
5. Certificate Chain Problems
If intermediate or root certificates are missing, the client may not trust the responder’s signature, leading to a failure even if the responder’s reply is otherwise valid.
Step‑by‑Step Troubleshooting Process
Follow this sequence to isolate and fix the OCSP response error.
- Verify the Certificate’s OCSP URL:
- Use
openssl x509 -in cert.pem -noout -textto inspect theAuthority Information Accesssection. - Confirm the URL resolves to the expected CA server.
- Use
- Test Connectivity to the Responder:
- Run
curl -v https://ocsp.example.comfrom the client host. - Check for TCP connect, TLS handshake, and HTTP response codes.
- Run
- Check System Clock:
- Synchronize the client’s time with a reliable NTP server.
- On Linux,
timedatectl set-ntp trueensures automatic sync.
- Validate the OCSP Response Manually:
- Retrieve the response:
openssl ocsp -issuer ca.pem -cert cert.pem -url https://ocsp.example.com -CAfile ca.pem -resp_text -noverify. - Review the output for errors such as
Response not validorSignature verification failed.
- Retrieve the response:
- Inspect Proxy and Firewall Rules:
- Ensure that outbound traffic to the responder port (usually 80 or 443) is allowed.
- Check for any proxy that rewrites or blocks the OCSP URL.
- Update or Replace the Certificate:
- If the OCSP URL is obsolete, obtain a new certificate from the CA with the correct responder.
- Verify that intermediate certificates are included in the chain.
Tools and Commands to Verify OCSP Status
Below are a few handy utilities that make diagnosing OCSP problems quicker.
- OpenSSL –
openssl ocspcan fetch and display raw responses. - SSLCertCheck – a lightweight script that checks certificate status against multiple CAs.
- nmap – with the
ssl-certscript to discover responder URLs automatically. - Browser DevTools – look at the
Securitytab for OCSP details and error logs.
Best Practices to Prevent Future Errors
- Keep system clocks tightly synchronized via NTP.
- Regularly audit certificates and their OCSP URLs.
- Deploy a local OCSP stapling cache if your environment has high latency to the CA.
- Configure firewalls to allow only the necessary OCSP ports and protocols.
- Implement automated monitoring that flags any certificate approaching revocation or expiration.
FAQ
- Why does my browser show “OCSP response not valid” but my server is fine?
Browsers enforce stricter OCSP checks and may reject responses that servers tolerate. Verify the browser’s console logs for additional details.
- Can I disable OCSP checks to bypass the error?
While disabling OCSP is possible in some clients, it removes a critical revocation check and is not recommended for production environments.
- What if the CA’s OCSP responder is down?
Most CAs provide a backup responder URL in the certificate. Use that URL or wait until the primary service resumes.
- How do I add the correct OCSP URL to an existing certificate?
You cannot modify a live certificate’s extensions; you must obtain a new certificate from the CA with the correct URL.
By systematically validating the responder URL, network paths, clock settings, and certificate chain, you can usually resolve “OCSP response not valid” errors quickly and restore secure connectivity.