Decoding OSCOSCPSC, OSS Gartner, SCSSESC and the CFO Role
When senior leaders talk about understanding OSCOSCPSC, OSS Gartner, SCSSESC and the CFO, the conversation can feel like a code‑cracking session. These abbreviations pop up in boardrooms, tech roadmaps, and ESG reports, yet many professionals only glimpse their surface meaning. This article unpacks each term, explains how they intersect in modern enterprises, and shows why the CFO’s perspective is increasingly central to navigating them.
What Is OSCOSCPSC?
OSCOSCPSC is an internal framework many large‑scale IT departments use to standardize operating‑system configuration and service‑control processes. In plain English, it’s a checklist that ensures every server—whether on‑prem or in the cloud—follows a consistent set of security baselines, patch‑management routines, and performance‑tuning guidelines. Companies that adopt OSCOSCPSC often report smoother audits because the framework aligns with both ISO 27001 requirements and internal risk‑management policies.
The “PSC” suffix stands for “Process Standard Catalog,” a repository where teams document each step, from initial image creation to decommissioning. By treating the catalog as living documentation, organizations can quickly adapt to new OS releases without reinventing the wheel each time.
Who Is OSS Gartner?
“OSS Gartner” isn’t a single product; rather, it refers to the body of Gartner research focused on Operational Support Systems (OSS). Gartner’s analysts evaluate vendors that provide tools for network monitoring, service assurance, and fault management—critical components for telecoms, utilities, and any business that runs complex digital infrastructure.
When a CIO cites OSS Gartner, they’re usually pointing to a Magic Quadrant or a Critical Capabilities report that helps decide which platform best balances scalability, integration ease, and total cost of ownership. The guidance often influences budgeting cycles, making it a natural touchpoint for the CFO.
Deciphering SCSSESC
SCSSESC stands for “Supply‑Chain Sustainability and ESG Compliance.” It’s a cross‑functional initiative that merges traditional supply‑chain risk management with the growing demand for environmental, social, and governance (ESG) transparency. The framework asks companies to map every tier of their supplier network, assess carbon footprints, and verify labor‑practice standards.
In practice, SCSSESC drives the adoption of tools that track emissions per shipped unit, flag suppliers lacking certification, and generate reports for investors. Because ESG metrics increasingly affect credit ratings and access to capital, the CFO must ensure that compliance costs are justified by the financial upside of sustainable sourcing.
The CFO’s Expanding Mandate
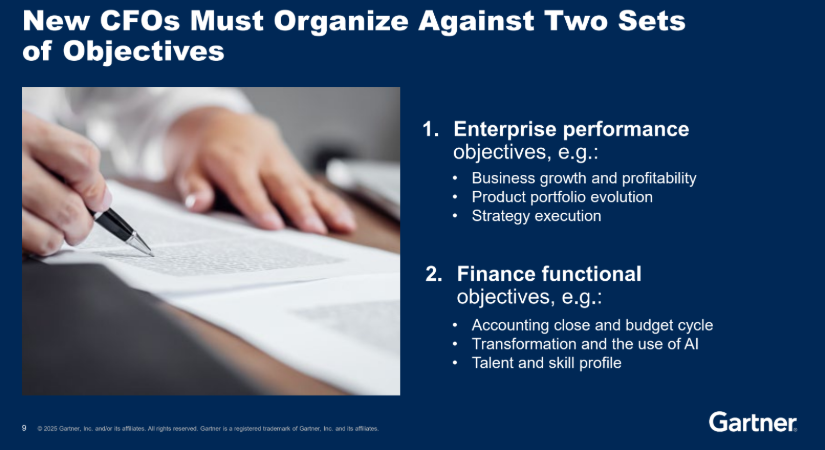
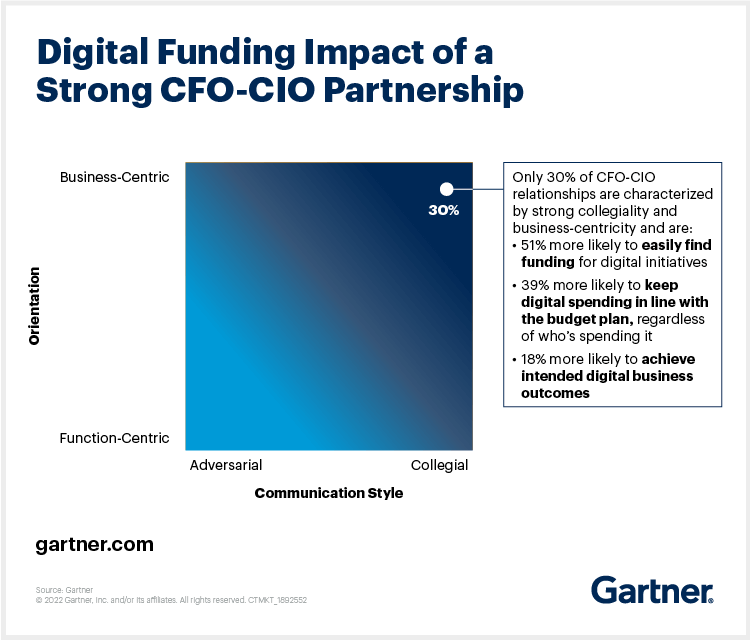
Historically, the Chief Financial Officer was the steward of balance sheets and cash flow. Today, the CFO also acts as a strategic bridge between finance, technology, and sustainability. When OSCOSCPSC demands investment in automation, OSS Gartner recommendations shape procurement, and SCSSESC introduces new reporting obligations, the CFO evaluates the ROI of each decision.
Key responsibilities now include:
- Quantifying the cost savings from standardized OS configurations versus ad‑hoc patching.
- Assessing the financial impact of choosing a Gartner‑rated OSS vendor—considering licensing, integration, and long‑term support.
- Modeling ESG‑related expenses and projecting how they affect investor sentiment and financing terms.
By translating technical jargon into dollar terms, the CFO helps the board make informed choices that align with both operational resilience and market expectations.
How the Pieces Fit Together
Imagine a telecom operator rolling out a new 5G core network. The project team first consults OSS Gartner to select a network‑management platform that scores high on scalability. Simultaneously, the IT department applies OSCOSCPSC to lock down the operating systems on every edge device, ensuring they meet security benchmarks. Meanwhile, the procurement group uses SCSSESC to verify that each hardware supplier adheres to carbon‑reduction targets.
The CFO reviews the combined budget, weighing the upfront spend against projected reductions in downtime, regulatory penalties, and ESG‑linked financing incentives. This holistic view illustrates why understanding each acronym isn’t just academic—it directly influences the company’s bottom line.
Common Pitfalls to Avoid
While each framework offers clear benefits, organizations often stumble when they treat them as siloed checkboxes. For example, implementing OSCOSCPSC without aligning it to the OSS vendor’s update cycle can create version‑conflict headaches. Likewise, pursuing SCSSESC compliance without involving finance may lead to “green‑washing” costs that never translate into measurable ESG scores.
To sidestep these traps, embed cross‑functional governance: a steering committee that includes the CIO, CFO, and sustainability lead can coordinate timelines, share data, and keep the initiative focused on value creation.
FAQ
What does OSCOSCPSC stand for and why does it matter?
OSCOSCPSC is a framework for standardizing operating‑system configuration and service‑control processes. It matters because it reduces security gaps, simplifies audits, and cuts the time spent on manual patching.
How can a CFO use Gartner’s OSS research?
The CFO can translate Gartner’s vendor ratings into financial risk assessments, comparing total cost of ownership, expected ROI, and potential savings from reduced downtime.
Is SCSSESC mandatory for all companies?
Not yet, but many investors and regulators now expect evidence of ESG compliance. Companies that adopt SCSSESC early often gain better financing terms and stronger brand reputation.
Can these frameworks be implemented separately?
Technically yes, but the greatest impact comes from integrating them—linking OS standards, OSS selection, and ESG supply‑chain checks under a unified financial oversight.