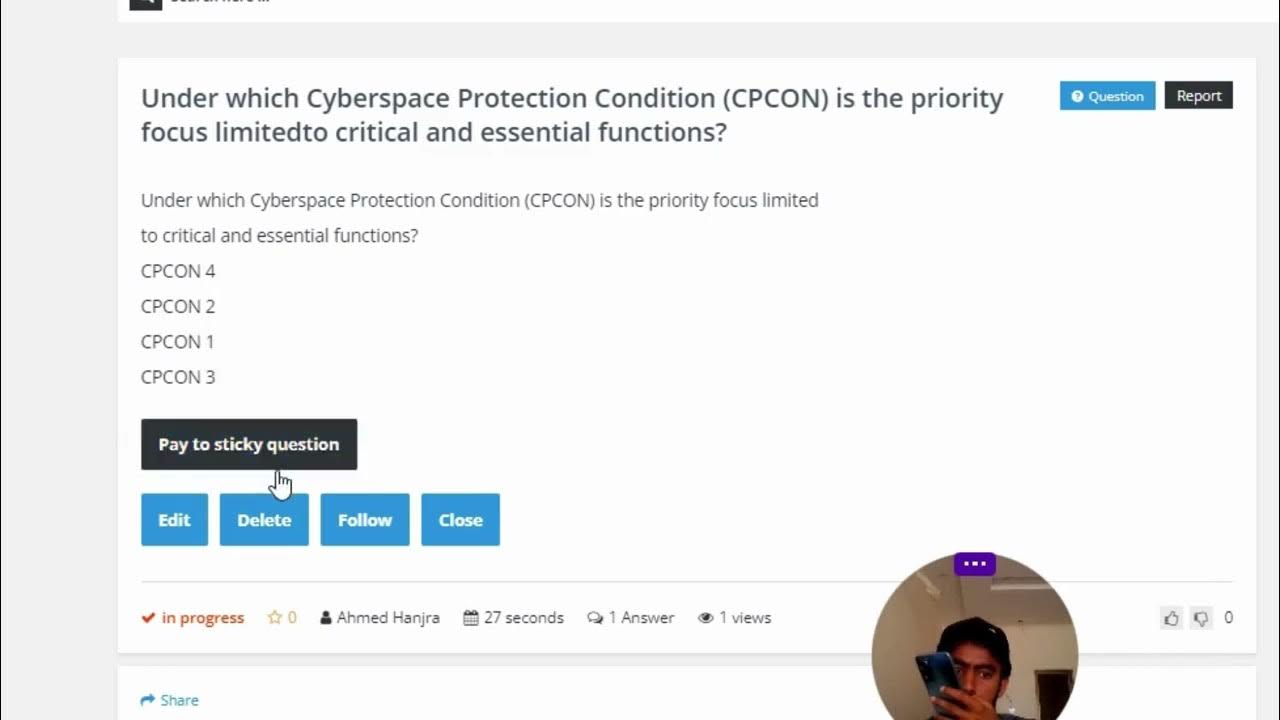
CPCon Explained: Pinpointing What’s Critical and Essential
When organizations talk about “critical and essential” components, they’re often referencing CPCon—a framework that helps teams separate what truly drives success from what merely supports it. Whether you’re managing a manufacturing line, a software rollout, or a public‑service operation, understanding CPCon can sharpen focus, reduce waste, and improve resilience. In the next few minutes we’ll unpack the basics, walk through the key steps, and see how the approach plays out in real‑world scenarios.
Why Critical and Essential Distinctions Matter in CPCon
At its core, CPCon (Critical‑Process‑Control) asks two questions: which processes cannot fail without jeopardizing the whole system, and which elements are indispensable for meeting core objectives? The answer guides resource allocation, risk mitigation, and performance monitoring. By labeling a task “critical,” you flag it for heightened oversight; labeling something “essential” tells you it must exist, though it may tolerate more flexibility.
Getting Started: The Four‑Phase CPCon Workflow
- Scope Definition – Map out the entire system, from inputs to outputs, and note every stakeholder.
- Criticality Assessment – Use impact analysis (e.g., failure mode impact, financial loss, safety risk) to rank each component.
- Essentiality Verification – Confirm that each “essential” element aligns with regulatory, contractual, or mission‑critical requirements.
- Control Implementation – Deploy monitoring, redundancy, or contingency plans based on the rankings.
This sequence isn’t linear; you may circle back to earlier steps as new data surfaces. The flexibility is intentional, allowing CPCon to adapt to evolving environments.
Tools and Techniques for Identifying Critical Items
Many teams start with a simple matrix: rows list processes, columns capture potential impacts like safety, cost, and reputation. Assigning a low‑medium‑high score makes the “critical” line visible at a glance. For more sophisticated settings, fault‑tree analysis or Monte‑Carlo simulations can quantify risk probabilities, but the underlying principle remains the same—focus attention where failure would be most damaging.
It’s also helpful to involve cross‑functional stakeholders. Engineers may see technical bottlenecks, while finance professionals spot cost‑center vulnerabilities. This broader view reduces blind spots that often hide in siloed assessments.
Essential Elements: Meeting the “Must‑Have” Bar
Essential components differ from critical ones in that they are non‑negotiable for compliance or core functionality, but they might not cause catastrophic failure if they falter temporarily. Think of a company’s legal compliance system: without it, you risk penalties, yet a brief outage could be managed with manual workarounds.
To verify essentiality, ask: “Can the organization operate without this element for a short period?” If the answer is “no,” you’re likely dealing with a critical item. If “yes, with effort,” it falls into the essential category. This simple test keeps the classification process grounded.
Balancing Resources: Prioritizing Investments
Once you’ve plotted critical and essential items, the next step is budgeting. Critical processes usually merit redundancy—duplicate hardware, parallel teams, or automated fail‑over. Essential items often get robust documentation, regular audits, and training programs to ensure they stay functional.
Remember, over‑engineering can be costly. Not every critical task needs a full‑scale backup; sometimes a well‑designed alert system suffices. The CPCon framework encourages you to match the level of control with the level of risk, rather than applying a one‑size‑fits‑all solution.
Real‑World Example: A Mid‑Size Manufacturing Firm
Consider a mid‑size plant that produces custom metal parts. Using CPCon, the team first mapped every step—from raw‑material receipt to final inspection. The welding station emerged as a critical process because a defect could compromise safety certifications and trigger costly rework. Meanwhile, the inventory tracking spreadsheet, while essential for order accuracy, was deemed non‑critical; a temporary manual log could keep the line moving.
Armed with this insight, the plant invested in a redundant welding robot and a real‑time sensor network to monitor temperature spikes. For the spreadsheet, they instituted a weekly backup routine and cross‑trained two staff members. Within six months, downtime dropped by 18 % and on‑time delivery improved, illustrating how CPCon’s focus on “critical and essential” can translate into measurable gains.
Common Pitfalls to Watch Out For
Confusing “critical” with “essential.” It’s easy to lump the two together and end up over‑protecting low‑impact items. Keep the impact‑severity lens sharp.
Neglecting periodic reviews. Systems evolve; a process once critical may become routine after automation, while new regulations can elevate an essential function to critical status.
Skipping stakeholder input. Decisions made in isolation often miss hidden dependencies that only surface when diverse voices are heard.
Maintaining CPCon Over Time
Implementing CPCon is not a one‑off project; it’s a continuous mindset. Schedule quarterly “critical‑essential” reviews, update matrices, and adjust controls as technology or market conditions shift. Embedding the framework into existing governance structures—like risk committees or operational review boards—helps keep it top of mind.
Finally, foster a culture that values transparency. When teams understand why a process is labeled critical, they’re more likely to report anomalies early, reducing the chance of surprises.
FAQ
What types of organizations benefit most from CPCon? Any operation that relies on multiple interdependent processes—manufacturing, IT services, healthcare, and logistics—can gain clarity and risk reduction from the framework.
How does CPCon differ from traditional risk assessments? Traditional assessments often look at hazards in isolation. CPCon adds a layer that distinguishes between “cannot‑fail” (critical) and “must‑have” (essential), guiding more nuanced control strategies.
Can CPCon be applied to small teams? Absolutely. Even a five‑person startup can map its core workflows, flag the most vulnerable steps, and set up simple redundancies or backup plans.
Is specialized software required? Not necessarily. Spreadsheets, whiteboards, and basic project‑management tools can support the initial phases. Larger enterprises sometimes adopt dedicated risk‑management platforms for scalability.